AGENT CONSOLE/
QUICK ACCESS
ACTIONS
↑↓Navigate↵OpenEscClose
AI INFRASTRUCTURE & SYSTEMSSECURITY GOVERNANCEAI AGENTS & MCP

MASOUD
ZEYNALI

AI InfrastructureAI Agents & MCPSystems Engineering

Senior AI Engineer — Agents, MCP & Infrastructure

Nearly two decades of enterprise IT and infrastructure engineering experience, combined with senior AI engineering focused on AI agents, Model Context Protocol (MCP), infrastructure automation, and secure AI-assisted operations.

AI / MCPConceptual portfolio map

InfraForge

CONTROL & CONTEXT LAYER

ASSISTED WORKFLOW · CONTROL & CONTEXT LAYER · RESTRICTED SSH INTERFACE · SERVER TARGETS · STRUCTURED INFRASTRUCTURE CONTEXT

Click the image for more information

Explore full project details
ENTERPRISE INFRASTRUCTURE FOUNDATION
DOMAIN::INFRA_SYSTEMS
~20YEARS
ENTERPRISE INFRASTRUCTURE
Continuous enterprise systems engineering & operations
LEADERSHIP::TEAM_GOV
30+
TECHNICAL TEAM SUPERVISED
Direct supervision of engineers, administrators & IT specialists
SCALE::ENDPOINT_OPS
300+
MANAGED WINDOWS ENDPOINTS
Centralized Active Directory, Group Policy & endpoint management

Explore my work

Featured technologies
  • Go
  • .NET
  • Next.js
  • PostgreSQL
  • Linux
  • MCP
  • OpenFlows Sewer
  • AutoCAD 2021
  • WPF
All technologies
RECRUITER FAST SCAN
Senior AI Engineer — Agents, MCP & Infrastructure
FOCUS
AI Infrastructure · AI Agents & MCP · Systems Engineering
FOUNDATION
Nearly two decades of enterprise IT and infrastructure engineering experience
OPERATING SCALE
30+ technical staff and specialists supervised · 300+ managed Windows endpoints
CURRENT ROLE
Deputy Head of Information Technology Department
LOCATION
Tehran, Iran
01 / PROFILE|SYSTEMS ARCHITECTURE

ENGINEERING EVOLUTION & TECHNICAL GOVERNANCE

Hands-on operational roots to enterprise IT leadership.

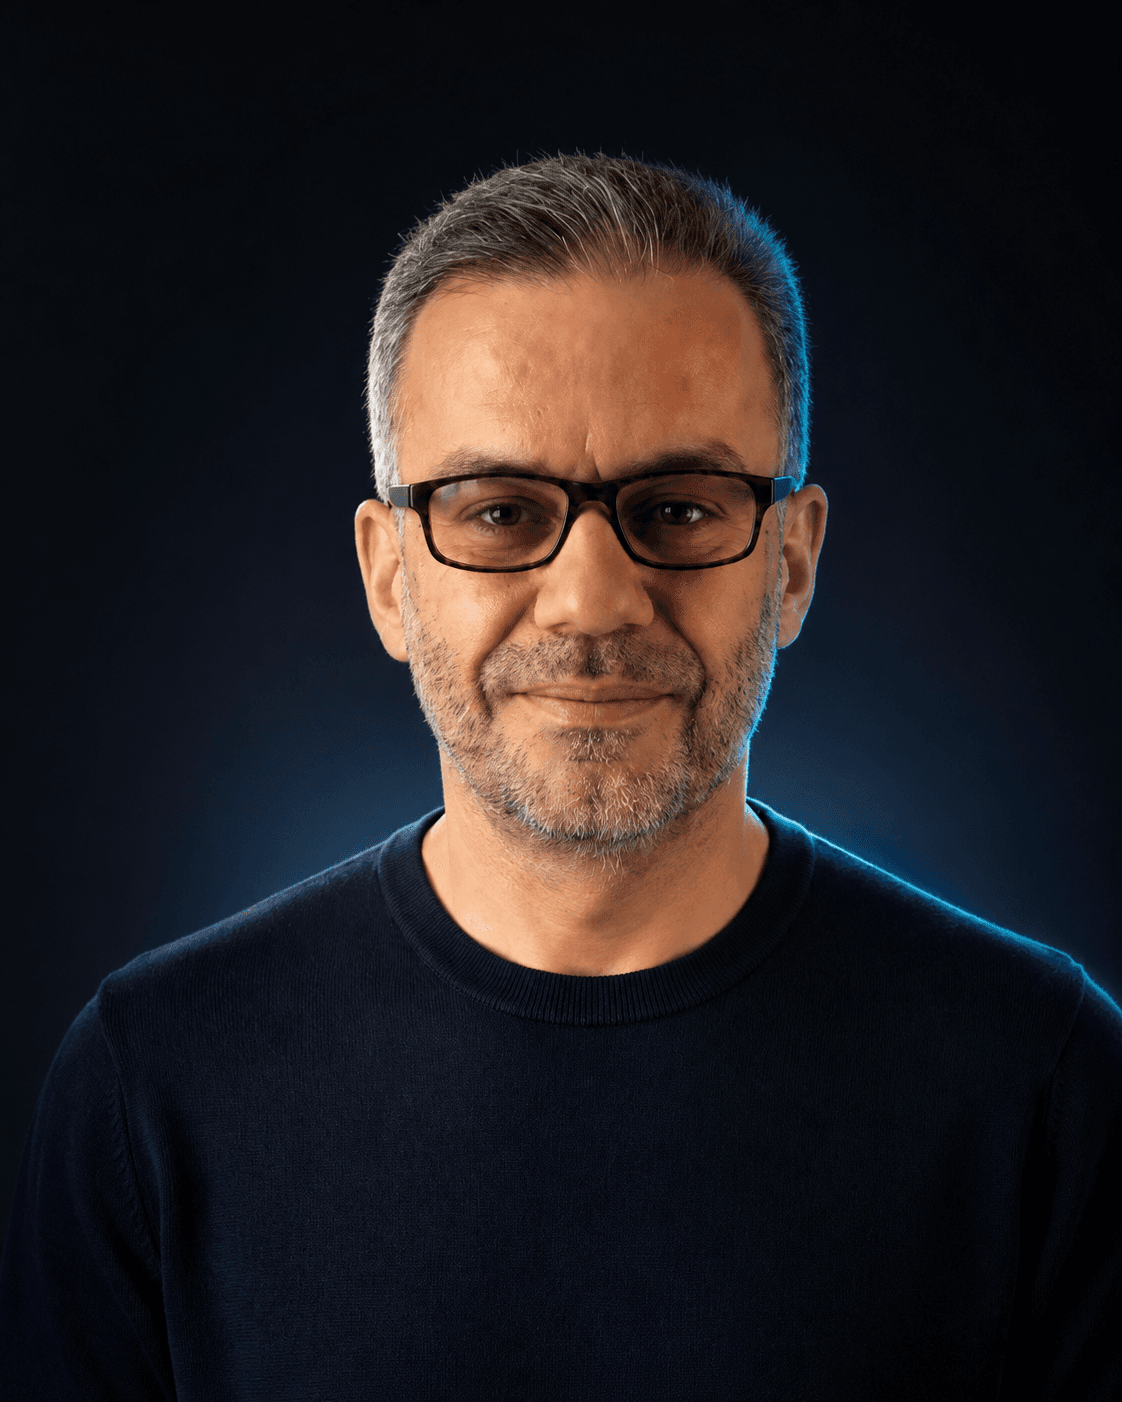
Portrait of Masoud Zeynali

Masoud’s career began in hands-on IT support, troubleshooting, and network operations, building a practical foundation across Windows client environments, Active Directory support, Group Policy, and organization-wide incident resolution. His responsibilities later expanded into the design and management of enterprise network infrastructure, administration and security of enterprise server environments, and centralized endpoint operations across more than 300 Windows endpoints.

As his responsibilities grew, Masoud moved into IT leadership and departmental responsibility, leading infrastructure development planning, defining the organization’s technology roadmap, supervising critical technology projects, and guiding more than 30 technical staff and specialists across network, security, help desk, and infrastructure functions. Today, nearly two decades of enterprise IT, infrastructure governance, and network security leadership serve as the foundation for his current engineering direction as a Senior AI Engineer—focused on AI agents, Model Context Protocol (MCP), infrastructure automation, and secure AI-assisted operational workflows.

ENGINEERING DISCIPLINES & PRINCIPLESCORE TENETS
INFRA::RELIABILITY
RELIABILITY

Infrastructure should remain stable and operational.

SECURITY::DESIGN
SECURITY

Infrastructure and network decisions should be security-conscious.

OPS::AUTOMATION
AUTOMATION

Recurring operational processes should be automated where appropriate.

LEADERSHIP::OUTCOMES
LEADERSHIP

Technical decisions should translate into practical organizational outcomes.

02 / CAREER|PROFESSIONAL TRAJECTORY

CAREER JOURNEY & LEADERSHIP PROGRESSION

Continuous progression across nearly two decades of professional IT experience, advancing from hands-on IT support and network operations to infrastructure ownership and departmental leadership.

Tehran Raymand Consulting Engineers
2007 — Present
Tehran, Iran
STAGE 01 · OPERATIONAL FOUNDATION
6 years

Help Desk and Network Support Specialist

Built a hands-on support foundation through technical troubleshooting, network infrastructure support, Active Directory services, and Windows client environments.

KEY RESPONSIBILITIES & SCOPE:
  • Technical support and advanced troubleshooting for network infrastructure, Active Directory services, and Windows client environments.
  • Implementation and management of centralized Group Policy Objects (GPO) and resolution of organization-wide hardware and software incidents.
  • Handling user requests and support tickets while improving the consistency, response quality, and reliability of IT support services.
STAGE 02 · INFRASTRUCTURE OWNERSHIP
7 years

Network Manager

Designed, implemented, and managed the company’s network architecture while maintaining the availability, stability, and security of critical internal services.

KEY RESPONSIBILITIES & SCOPE:
  • Administration and security of enterprise server environments, including Microsoft Exchange and MDaemon.
  • Sophos Firewall administration for traffic control, monitoring, NAT, policy enforcement, and perimeter protection.
  • Centralized administration of more than 300 Windows endpoints, including patch management, software distribution, and automation through ManageEngine Endpoint Central.
VERIFIED SCALE:300+ Windows endpoints
STAGE 03 · IT LEADERSHIP
Last 5 years — Present

Deputy Head of Information Technology Department

Leads the IT department, plans infrastructure development, defines the organization’s technology roadmap, and supervises critical technology projects while contributing to resource allocation, IT budgeting, and technology lifecycle oversight.

KEY RESPONSIBILITIES & SCOPE:
  • Direct supervision, evaluation, and guidance of more than 30 employees, senior specialists, and technical professionals across network, security, help desk, and infrastructure functions.
  • Infrastructure development planning, technology roadmap definition, and oversight of critical technology projects.
  • Resource allocation, contribution to IT budgeting, technology asset lifecycle oversight, and development of the team’s technical capabilities.
VERIFIED SCALE:30+ technical staff and specialists
03 / EXPERTISE|TECHNICAL MATRIX

TECHNOLOGY LANDSCAPE

A structured engineering matrix spanning enterprise platforms, network security, messaging, edge and cloud infrastructure, endpoint governance, and senior AI engineering across agents and Model Context Protocol (MCP).

01DOMAIN

INFRASTRUCTURE & PLATFORMS

Administration and operation of Windows Server and Linux environments, with Active Directory, Group Policy, Docker, and supporting enterprise services.

  • Windows Server
  • Linux
  • Active Directory
  • Group Policy
  • Docker
02DOMAIN

NETWORKING & SECURITY

Network security and traffic administration spanning firewall policy, NAT, DNS, SSH, defensive controls, network monitoring, and connectivity technologies.

  • Sophos Firewall
  • NAT
  • DNS
  • SSH
  • Fail2ban
  • Network Monitoring
  • V2Ray / VLESS
03DOMAIN

MESSAGING & COLLABORATION

Administration of enterprise messaging environments and secure mail infrastructure across Microsoft Exchange, MDaemon, Mailcow, and SSL/TLS certificate operations.

  • Microsoft Exchange
  • MDaemon
  • Mailcow
  • SSL / TLS
04DOMAIN

WEB & CLOUD

Linux web services and cloud-based traffic management using Nginx, Caddy, Cloudflare DNS, Cloudflare Workers, redirects, and domain forwarding.

  • Nginx
  • Caddy
  • Cloudflare DNS
  • Cloudflare Workers
  • Redirects
  • Domain Forwarding
05DOMAIN

ENDPOINT OPERATIONS

Centralized Windows endpoint administration at 300+ device scale, covering patch management, software distribution, automation, and operational control with ManageEngine Endpoint Central.

  • ManageEngine Endpoint Central
  • Windows Endpoints
  • Patch Management
  • Software Distribution
  • Endpoint Automation
VERIFIED SCALE:300+ WINDOWS ENDPOINTS
06DOMAIN

AI ENGINEERING, AGENTS & MCP

Senior AI engineering focused on agentic systems, Model Context Protocol (MCP), LLM-assisted infrastructure operations, operational reasoning, and automation across modern infrastructure workflows.

  • AI Agents
  • Agentic Workflows
  • Model Context Protocol (MCP)
  • Large Language Models
  • LLM Integration
  • Infrastructure Automation
  • Operational Reasoning
  • Log Analysis
  • AI-assisted Troubleshooting
  • Tool Integration
  • Context Engineering
  • Scripting & Automation
04 / SELECTED WORK|CASE STUDY

ENGINEERING IN PRACTICE

Selected engineering work illustrating AI engineering at the infrastructure boundary—where systems operations, security controls, and agentic workflows converge.

PROJECT INDEX / 02—0807 / ADDITIONAL PROJECTS

MORE SYSTEMS. REAL ENGINEERING BOUNDARIES.

Seven additional projects across on-prem operations, observability, engineering applications and document workflows. Statuses describe verified milestones—not a claim that every feature is production-ready.

PROJECT / 02

ON-PREM IT OPERATIONS

Ops

An offline-first operations and diagnostic control plane

A single-server operations platform bringing infrastructure diagnostics, asset context and gated automation into a controlled on-prem environment. Server health is sourced through a separate monitoring service; endpoint integrations remain independently scoped.

SYSTEM FLOW
  1. Operator / API
  2. On-prem service
  3. PostgreSQL & audit
  4. Gated diagnostics
TECHNOLOGIES & DOMAIN
  • Go
  • PostgreSQL
  • REST API
  • Linux
  • RBAC
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Bring together operational context without giving an automation agent unrestricted access or making cloud connectivity a requirement.

ARCHITECTURAL APPROACH

Separate server monitoring from endpoint collection; require explicit authorization, durable audit and fail-closed diagnostic behavior.

VERIFIED MILESTONE / LIMITATION

On-prem PostgreSQL migrations, repeatability and audit / denial tests passed acceptance. Additional integrations remain part of ongoing engineering work.

IN DEVELOPMENT
PROJECT / 03LINUX PILOT · ACCEPTED

INFRASTRUCTURE OBSERVABILITY

Probe

Independent server monitoring through a controlled API

A dedicated monitoring service for Linux infrastructure with structured health data, persistence and operational history. Designed to remain independent while exposing infrastructure context to permitted REST consumers.

SYSTEM FLOW
  1. Linux targets
  2. Probe collection
  3. Persisted history
  4. REST consumers
TECHNOLOGIES & DOMAIN
  • Linux
  • PostgreSQL
  • REST
  • Monitoring
  • Audit
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Collect useful operational evidence without coupling the monitoring lifecycle to a larger IT management product.

ARCHITECTURAL APPROACH

Treat monitoring as a separate service with controlled access, history retention and tested backup / restore behavior.

VERIFIED MILESTONE / LIMITATION

Linux-only pilot acceptance closed successfully. Windows pilot coverage was deferred and is not presented as validated.

PROJECT / 04

ENGINEERING SOFTWARE INTEGRATION

SewerPilot

A version-tolerant interface to OpenFlows Sewer models

A desktop engineering workbench that interacts with OpenFlows Sewer through a guarded adapter layer. The confirmed real-runtime path reads conduit and structure information without modifying the source model.

SYSTEM FLOW
  1. OpenFlows runtime
  2. Capability adapter
  3. Read-only model intake
  4. Desktop workspace
TECHNOLOGIES & DOMAIN
  • C# / .NET
  • OpenFlows Sewer
  • Adapter Contracts
  • Desktop UI
  • Model Integrity
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Integrate with a specialized engineering runtime without binding the product to one fixed vendor assembly shape or risking a live model.

ARCHITECTURAL APPROACH

Discover capabilities at runtime, gate unproven write and solver operations, and validate model integrity with unchanged source hashes.

VERIFIED MILESTONE / LIMITATION

Real-runtime read-only model access was proven; intake and automated regression checks also passed. Full graphical workflows and live engineering execution are separately validated before release.

IN DEVELOPMENT
PROJECT / 05DESKTOP CORE · VALIDATED

DOCUMENT ENGINEERING / COMPLIANCE

DccSentry

Offline document compliance and review workflow

A Windows desktop tool for checking engineering document packages against numbering, register and compliance rules, then presenting traceable findings for human review.

SYSTEM FLOW
  1. Document packages
  2. Local parsers / OCR
  3. Compliance checks
  4. Findings & review
TECHNOLOGIES & DOMAIN
  • C# / .NET
  • WPF
  • Tesseract
  • PDFium
  • Excel / PDF
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Detect document-control issues in mixed PDF and spreadsheet inputs without relying on remote OCR or external SaaS.

ARCHITECTURAL APPROACH

Prefer native text extraction, use offline OCR only as fallback, and keep findings reviewable with explicit provenance.

VERIFIED MILESTONE / LIMITATION

Offline OCR and core desktop workflows have recorded passing acceptance and release milestones; this does not imply that every later release gate passed.

PROJECT / 06REAL-DWG PILOT · REVIEW-GATED

CAD QUALITY ASSURANCE

EngiSentry

Read-first engineering checks for complex AutoCAD drawings

An AutoCAD-oriented engineering validation suite covering drawing inspection, equipment association, semantic checks and plotting-related QA. Ambiguous relationships are surfaced for review instead of silently resolved.

SYSTEM FLOW
  1. AutoCAD drawing
  2. Read-only inspection
  3. Semantic / QA engine
  4. Review evidence
TECHNOLOGIES & DOMAIN
  • AutoCAD 2021
  • C# / .NET
  • DWG
  • Semantic QA
  • Drawing Validation
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Turn inconsistent drawing geometry and annotations into actionable engineering findings without making unsafe assumptions.

ARCHITECTURAL APPROACH

Apply fail-closed checks and human review for uncertain equipment associations; protect source drawings during inspection.

VERIFIED MILESTONE / LIMITATION

Regression suites and real-DWG pilot checks ran successfully. The pilot still exposed incomplete and ambiguous associations requiring review.

PROJECT / 07v1.0.5 · RELEASE VERIFIED

CONSTRUCTION ESTIMATION

BaravardYar

A Persian desktop estimator grounded in official price books

A Windows estimation application built around packaged 1404 construction and roadwork price-book data, with rule-driven calculations and a Persian operator interface.

SYSTEM FLOW
  1. Official price books
  2. Rules & coefficients
  3. Estimate calculation
  4. Persian desktop UI
TECHNOLOGIES & DOMAIN
  • .NET
  • Windows Desktop
  • 1404 Price Books
  • Rules Engine
  • Persian UI
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Make estimates reproducible and inspectable while keeping reference data and calculation rules explicit.

ARCHITECTURAL APPROACH

Package source datasets with the application, separate rules from UI behavior and run deterministic regression checks.

VERIFIED MILESTONE / LIMITATION

Version 1.0.5 Windows release and a 576-test regression run passed. Optional regional factors remain a separately tracked scope.

PROJECT / 08

CAD PLOTTING AUTOMATION

PlotWise

Controlled plotting workflows for engineering DWG files

An AutoCAD plot-planning project intended to reduce manual print preparation and improve repeatability across drawing-based deliverables.

SYSTEM FLOW
  1. DWG source
  2. Plot planning rules
  3. Controlled operations
  4. Pilot validation
TECHNOLOGIES & DOMAIN
  • AutoCAD 2021
  • DWG
  • Plot Planning
  • QA
  • Desktop Automation
EXPLORE ENGINEERING DOSSIER
ENGINEERING PROBLEM

Translate drawing-specific plotting decisions into a repeatable, inspectable workflow rather than a fragile series of manual operations.

ARCHITECTURAL APPROACH

Break delivery into bounded acceptance stages and keep an explicit distinction between completed phases and blocked pilot work.

VERIFIED MILESTONE / LIMITATION

Multiple scoped implementation phases closed successfully. Plot-planning behavior continues through controlled pilot acceptance; no general-availability release is claimed.

IN DEVELOPMENT

Public engineering summaries only. Private source code, infrastructure identifiers, client models and operational secrets are intentionally excluded.

SYSTEMS ARCHITECTURE|MCP & CONTROL BOUNDARIES|

AI AGENTS AT THE INFRASTRUCTURE BOUNDARY

Architectural analysis of Model Context Protocol (MCP) integration with Linux infrastructure—focusing on least-privilege operations, credential isolation, and explicit control boundaries.

OPERATIONAL CONTROL FLOW & ACCESS BOUNDARIES/MCP INTEGRATION PATTERN
  1. 01OPERATOR INTENT

    AI / MCP CLIENT

    Agent receives an infrastructure task and formulates structured MCP tool invocation requests.

  2. 02CONTROL & SCHEMA LAYER

    MCP SERVER BOUNDARY

    InfraForge validates tool inputs against structured schemas and enforces defined operational scope.

  3. 03ISOLATION & VALIDATION

    CREDENTIAL HANDLING

    Server-specific SSH credentials and keys are validated for the requested operation, avoiding persistent exposure in model context.

  4. 04INFRASTRUCTURE ACCESS

    LINUX TARGET INTERFACE

    Restricted SSH sessions execute the requested task, maintaining clear boundaries between monitoring and administrative workflows.

SECURITY & OPERATIONAL BOUNDARIES/DESIGN PRINCIPLES

Structured Tool Interface

EXECUTION CONTROL

Interactions rely on structured MCP tool contracts rather than treating unrestricted interactive shells as the default operating model.

Credential Hygiene & Isolation

ACCESS PROTECTION

SSH private keys and sensitive authentication material are treated as protected data and isolated from normal operational logs and agent prompts.

Monitoring & Administration Separation

LEAST PRIVILEGE

Read-only monitoring relies on restricted monitoring identities, while privileged administration requires separately validated and controlled access.

Controlled Telemetry & Log Handling

OBSERVABILITY

System metrics, service states, and journal outputs are handled with care to prevent sensitive configuration data from leaking into model context.

ARCHITECTURAL DESIGN DECISIONS/ENGINEERING JUDGMENT

Structured Tool Schemas vs. Direct Bash Execution

Allowing unrestricted command execution increases operational and injection risk. Enforcing structured tool schemas with explicit parameter constraints prioritizes predictability, auditability, and operational safety.

Per-Server Credential Validation vs. Centralized Agent Key Storage

Storing broad administrative keys in an open agent store creates a single point of failure. Implementing per-server credential validation and controlled enrollment helps contain the blast radius of operational actions.

05 / INTERACTIVE EXPERIENCE|BROWSER-ONLY SIMULATION

OPERATIONAL REASONING LAB

Explore how agentic requests translate into explicit operational boundaries, predictable system behavior, and safe AI-assisted infrastructure workflows.

SIMULATED INTERACTIVE DEMO

Browser-only demonstration. No live infrastructure connection, remote execution, application-level data request, or real server data is involved.

Select Scenario3 Scenarios Available
SCENARIO 01/STRUCTURED REASONING

DISCOVER INVENTORY

DISCOVERY
01 / REQUEST

Represent Linux infrastructure context as a structured inventory view.

02 / OPERATIONAL BOUNDARY

Remain within discovery and inventory scope. Do not treat unrestricted shell access as the default interaction model.

03 / EXPECTED SYSTEM BEHAVIOR

Represent infrastructure information as structured context that can be reviewed before any broader operational action is considered.

06 / CREDENTIALS & CONTACT|VERIFIED PROFESSIONAL RECORD

RESUME, CREDENTIALS & DIRECT CONTACT

A concise professional record combining verified credentials, education, and direct contact channels.

PROFESSIONAL RESUME

PDF / ENGLISH

Download the verified English professional CV used as a factual source for this portfolio.

MICROSOFT CERTIFICATIONS

  • MCSE: Server InfrastructureMicrosoft Certified Solutions Expert · Microsoft
    2012
  • MCSE: Cloud Platform and InfrastructureMicrosoft Certified Solutions Expert · Microsoft
    2016

EDUCATION

  • Master of Business Administration (MBA)University of Tehran
    IN PROGRESS
  • Associate Degree in Information Technology (IT)Karaj University

DIRECT CONTACT

Masoud Zeynali

Senior AI Engineer — Agents, MCP & Infrastructure

IT Manager | Network Infrastructure & Security Specialist

Tehran, Iran
MASOUD ZEYNALI :: SYSTEMS ENGINEERING
IT INFRASTRUCTURE · SECURITY · AI AUTOMATION© 2026

EVIDENCE LAYER

/
06 RECORDS
01 / 06·PROFESSIONAL RECORD
SELECTED

Enterprise IT & Infrastructure

CLAIM

Nearly two decades of enterprise IT and infrastructure engineering experience.

EVIDENCE BASIS

Professional timeline: Tehran Raymand Consulting Engineers, 2007–Present, across help desk and network support, network management, and IT department leadership.

DISCLOSURE

This reflects the professional record presented in this portfolio and CV; no independent third-party verification is claimed.

SOURCES
Download CV
02 / 06·PROFESSIONAL RECORD

Technical Team Leadership

CLAIM

30+ technical staff and specialists supervised.

EVIDENCE BASIS

Leadership scope includes network, security, help desk, and infrastructure staff and specialists within the IT department.

DISCLOSURE

This reflects the professional record presented in this portfolio and CV; no independent third-party verification is claimed.

SOURCES
Download CV
03 / 06·PROFESSIONAL RECORD

Windows Endpoint Operations

CLAIM

300+ managed Windows endpoints.

EVIDENCE BASIS

Endpoint administration experience includes centralized Windows endpoint management using Endpoint Central.

DISCLOSURE

This reflects the professional record presented in this portfolio and CV; no independent third-party verification is claimed.

SOURCES
Download CV
04 / 06·PROJECT EVIDENCE

AI Engineering · Agents · MCP

CLAIM

Engineering work focused on AI agents, Model Context Protocol (MCP), infrastructure automation, and operational reasoning.

EVIDENCE BASIS

InfraForge demonstrates MCP-enabled infrastructure tooling and AI-assisted operational workflows.

DISCLOSURE

Project evidence demonstrates engineering work; by itself, it does not independently establish employment duration or seniority.

SOURCES
Open GitHub Repository
05 / 06·PUBLIC PROJECT SOURCE

InfraForge

CLAIM

InfraForge — MCP-enabled infrastructure operations tooling.

EVIDENCE BASIS

The public GitHub repository and portfolio case study document the project's implementation and architecture.

DISCLOSURE

Repository contents are public project evidence; production usage or external adoption is not claimed unless explicitly documented.

SOURCES
Open GitHub Repository
06 / 06·OFFICIAL TRANSCRIPT

Microsoft Credentials

CLAIM

MCSE Server Infrastructure — 2012 · MCSE Cloud Platform and Infrastructure — 2016

EVIDENCE BASIS

The Microsoft Learn transcript is provided as the official credential source.

DISCLOSURE

Credential details should be interpreted exactly as shown in the linked Microsoft transcript.